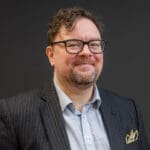
Jeff Watkins is a seasoned CTO and CPTO who has spent his career leading technology, product, and AI organisations through rapid growth and reinvention. He’s steered engineering, product, cloud, cybersecurity, and AI strategy teams through major transformations, turning ambitious ideas into secure, human-centred digital experiences for some of the world’s best-known brands.
A lifelong technologist, Jeff brings over 25 years of hands-on experience across financial services, healthcare, the public sector and retail. He’s founded and led multiple cybersecurity teams and is a vocal champion of secure-by-design practices for generative AI. With an MSc in Cybersecurity and a second Master’s in Artificial Intelligence underway, he’s currently researching anthropomorphised LLM agents and deception detection.
On the international circuit, Jeff is a sought-after keynote speaker, headlining events such as Webinale (Berlin), AppDevCon (Amsterdam), the International JavaScript Conference (London), and Edinburgh Napier’s PlusEquals5 summit. His candid, story-driven take on the collision of AI, cybersecurity, culture and human behaviour resonates with audiences from engineers to executives.
He also co-hosts the multi-award-winning Compromising Positions podcast, where he interviews psychologists, anthropologists, UX researchers and security leaders to bring fresh, outsider insight to cyber. His thought leadership has been featured in Wired, Forbes, Raconteur, IT Pro, Business Cloud, and Information Age, and he’s a regular commentator for the wider technology and security press.
Whether mentoring emerging leaders, building prototypes, or demystifying AI on stage, Jeff’s mission is simple: build technology that elevates people, never the other way around.
Generative AI is rapidly becoming embedded in software delivery pipelines through code copilots, third-party models, and autonomous agents that shape products in real-time. For technology leaders, this introduces a new class of risks that traditional secure SDLC practices don’t fully address: poisoned dependencies, model supply-chain vulnerabilities, opaque agent behaviour, and regulatory scrutiny.
In this session, we’ll examine the implications of both using your own AI models and consuming third-party ones, and what this means for the resilience and reputation of your organisation. Attendees will learn how to evolve their delivery lifecycle to account for AI, where governance must catch up, and how AI itself can play a role in defending the enterprise.
Key points covered:
Strategic Impact – AI changes the threat model of your delivery organisation; leaders must reassess governance and risk appetite.
Supply Chain Reality – Third-party AI models and agents become critical dependencies that require the same scrutiny as open-source packages.
Secure Evolution – The secure SDLC must evolve with AI: treat AI outputs as untrusted, enforce model provenance, and explore AI-enabled defences.